0

CEPT Certified!

-

I finally got the Certified Expert Penetration Tester (CEPT) with a good score on the practical. There were two parts to the certification : an objective multiple choice written test and a practical. To qualify one needs 70% on the written and 70% on the practical portion of the test.
The written test was not too challenging if you follow the material taught at the InfoSec Institute’s Advanced Ethical Hacking course, however, the practical made up on the lack of challenge. The practical involved writing an unpublished stack overflow exploit for a real-world commercial software of IACRB’s choosing, a format string exploit for a custom application and writing a patch for windows binary to subvert registration mechanism on the binary. One could write the exploit in the form of a python script (that I chose), a shell script , a perl script or a binary written in a language of our choosing. The solution could be quite flexible when it came to the choice of language for writing the exploits.
Personally speaking, this was a great learning experience for me and I plan to continue learning in the interesting field of vulnerability development!

3

West Coast to East Coast: antithetical US

-

A moratorium for 3 months on the blogspot. The things have changed dramatically when it comes to the life. A lot has happened in my life since the time I left Los Angeles, CA to come to New York, NY. The two of the biggest cities of not only the USA but in the world as well.
First things first…got a job for Ernst & Young’s Advanced Security Center and so like most of the people who work in New York I live in Jersey City, NJ and travel to work. The travel is not too bad as it takes about 45 mins door-to-door. Also, by living in New Jersey instead of 5 boroughs (New Yorkers call the collection of 5 islands of Manhattan, Queens, Brooklyn, Bronx, Statten Island as the 5 boroughs) one saves the 4% annual New York city tax.
Now for the topic of this blog which is “Moving”…which is probably the most troublesome experience that people have. It wasn’t too good for me either but it could have been worse if it were not for the help of some good friends. People say that you realize the truthfulness of your friends during the time of adversity. It was exactly what I found. Whereas some people came to the fore to help me in all the ways they could, some stayed at the bay (and in some cases … making sure that the buoy of my life was in doldrums). Well…having said that life is but a bunch of grapes … some sweet and some sour (this is something I heard in the Hindi Movie “Khatta Meetha”)!
Finding apartments in the New York area can be a harrowing experience, especially if you are hard strung on budget. That was exactly what I found. The best places to look for are New Jersey Craigslist and New York Craigslist. Other places are Rent.com and Apartments.com but I did not find them much useful. I found that New York had some really good places to rent even with a tight budget. All these places were in Queens (Rego Park, Forest Hills). The good part was one could get a 2BR for $1450+ in these places. These places were not too far from the Subway stations and had a travel of 40-45 mins to Manhattan and 1 hr to Long Island (using Long Island Rail Road aka LIRR).
Jersey City in NJ is also a very good bet. But there are some places in Jersey City that are posh as hell but you have to pay the price for the class. Exchange place and Pavonia/Newport are examples of these places (with prices around $1700 for 1 BR) . Grove street is also a place which is somewhere in between the posh and the not-at-all posh. Even though the prices in Exchange place and Newport are really high but the class is well worth the money. Especially when you consider that getting a similar type of apartment in Manhattan will cost at least twice or may be thrice as much. Another avenue for exploration is Hoboken, NJ. Hoboken was personally my favorite place to look for an apartment because it is a place with a vibrancy associated with it. Almost looks like a European city bustling with restaurants and youth on the streets! It is also not too far from New York. However just like Pavonia/Newport & Exchange Place this fun doesn’t come cheap! The apartment costs are similar. The difference between Newport – Exchange Place & Hoboken is that the construction in Hoboken is older and you need a realtor for getting an apartment more than you need in former. Realtors have standard 1 month rent as the fee as their service charges.
In case you are wondering what a realtor is – a realtor is a person who searches for an apartment for you that fits within your budget and choice. But when it comes to realtors one must be wary of them because they can sometimes be a dangerous bet to pick!
West coast was much easier to find apartments in from my experience but it could be because I was looking for apartments in a University area which is probably easier.

-Rajat
http://rajatswarup.blogspot.com/

1

Brand New Day

-

It’s a brand new day with no novelty! Back to the lab today trying to now get access to the packet data to calculate the hash values. I suspect that inside netfilter’s sk_buff structure there’s an unsigned char* data field. This probably is exactly what I need to get the hash values. There’s this awesome link which has great information about sk_buff structure. The unsigned int len; has the size of the complete input data including the headers. I guess if this len value == size of the actual data for the IP header (which could be TCP header / UDP header / ICMP header) then if we are using chunks of this data to find hashes then the following algorithm could be used:

no_of_chunks = len / BYTE_SIZE_FOR_SIGN;

addendum = len % BYTE_SIZE_FOR_SIGN;


for (int i = 0; i < no_of_chunks; i++)
{
storeInTable(hashRabin(data,i*BYTE_SIZE_FOR_SIGN,
(i+1)*BYTE_SIZE_FOR_SIGN - 1 ,0));
}
storeInTable(
hashRabin(data,no_of_chunks*BYTE_SIZE_FOR_SIGN,
no_of_chunks*BYTE_SIZE_FOR_SIGN+addendum, 0)
);


This are my initial thoughts let’s see how it works out!

-Rajat.
Rajat’s Homepage

0

Shmoocon in DC

-

I’ll be attending the Shmoocon in Washington, DC from Feb 6th-8th. Hope to see all you h4X0rs out there!

0

Batman Begins: Movie Review

-

I’ve been a Batman fan since the time my father took me to watch the first Batman movie starring Michael Keaton. The latest addition to the Batman series is Christopher Nolan’s Batman Begins. The film is an excellent depiction of Batman and his rise as the caped crusader in Gotham City. The story is a prequel to the Batman movies which we have seen in the past.
The remaining cast is also well studded with some of the best actors of Hollywood like Michael Caine (Alfred) and Morgan Freeman. Katie Holmes also has done a good job of acting. But I still think that Michelle Pfeiffer is yet to be beaten in looks in the entire Batman series.
Overall, the movie is excellent with everything about Batman being explained and I think it’s a must watch for any Batman fan!

2

Bit of Forensics

-

I like using dcfldd for creating the raw images, because it shows a nice status…it’s interesting to see progress.

dcfldd if=/dev/sda of=/mnt/sdb1/filename.dd hash=md5 md5log=hashfile.md5 conv=noerror,sync bs=4096

It’s the ‘bs’ (stands for bytesize) that makes the difference (…always does doesn’t it ;-).

Autopsy – The forensics browser always uses the ~/.autopsy as the base directory for storing the files from the cases. The following command is helpful in changing the directory in which the cases should be stored:

./autopsy -d /mountpoint/dirname

The exiftool is a cool application that can read meta-information to determine the different types of files.

0

PCI SSC Forbids SSL and “Early TLS”

-

On April 15, 2015 the PCI SSC released the PCI DSS v3.1.  The main cause for concern for most merchants and other entities (called “entities” hereonforth) that store, transmit and process cardholder data is the prohibition of using SSL and “Early TLS”.  The PCI SSC also released a supplement to assist entities in mitigating the issue.   The supplement references the NIST guideline SP800-52 rev1 for determining which are good ciphers and which are not.

The key point being what does “Early TLS” mean?  Does it mean TLSv1.0 and TLSv1.1 OR does it mean only TLSv1.0?  Are the entities supposed to disable all ciphers except anything that’s TLSv1.2?

Answer is (in consultant speak) “it depends”. 🙂

TLSv1.1 does theoretically have ciphers that are not ideal.  Example: CBC mode ciphers that are TLSv1.1 but there may be a potential for attacks on them given that in the past couple of years CBC has fallen multiple times (BEAST, POODLE).

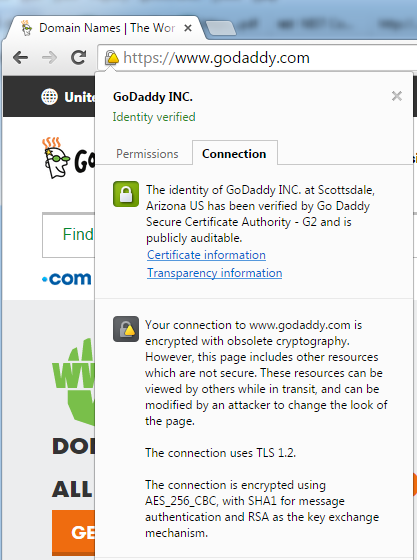
Google Chrome lists the use of CBC-based ciphers (despite the fact that they’re TLSv1.1) to be obsolete.  Google Chrome essentially makes “obsolete cryptography” a function of using TLS v1.2-based ciphers.
Untitled2

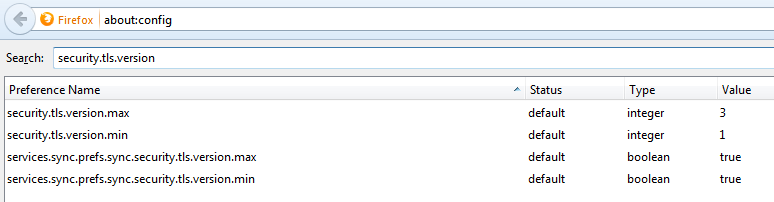
Firefox allows the configuration of disabling TLSv1.0 and that can be done by typing “about:config” in the address bar.  The security.tls.version.min = 0 (means SSLv3), 1 (means TLSv1.0), 2 (means TLSv1.1) and 3 (means TLSv1.2).  The following screenshot shows the configuration snapshot (here the lowest allowed version is TLSv1.0).
Untitled3

Let’s start with what is definitely ok for PCI:

https://www.openssl.org/docs/apps/ciphers.html#TLS-v1.2-cipher-suites

 TLS_RSA_WITH_NULL_SHA256                  NULL-SHA256
 TLS_RSA_WITH_AES_128_CBC_SHA256           AES128-SHA256
 TLS_RSA_WITH_AES_256_CBC_SHA256           AES256-SHA256
 TLS_RSA_WITH_AES_128_GCM_SHA256           AES128-GCM-SHA256
 TLS_RSA_WITH_AES_256_GCM_SHA384           AES256-GCM-SHA384

 TLS_DH_RSA_WITH_AES_128_CBC_SHA256        DH-RSA-AES128-SHA256
 TLS_DH_RSA_WITH_AES_256_CBC_SHA256        DH-RSA-AES256-SHA256
 TLS_DH_RSA_WITH_AES_128_GCM_SHA256        DH-RSA-AES128-GCM-SHA256
 TLS_DH_RSA_WITH_AES_256_GCM_SHA384        DH-RSA-AES256-GCM-SHA384

 TLS_DH_DSS_WITH_AES_128_CBC_SHA256        DH-DSS-AES128-SHA256
 TLS_DH_DSS_WITH_AES_256_CBC_SHA256        DH-DSS-AES256-SHA256
 TLS_DH_DSS_WITH_AES_128_GCM_SHA256        DH-DSS-AES128-GCM-SHA256
 TLS_DH_DSS_WITH_AES_256_GCM_SHA384        DH-DSS-AES256-GCM-SHA384

 TLS_DHE_RSA_WITH_AES_128_CBC_SHA256       DHE-RSA-AES128-SHA256
 TLS_DHE_RSA_WITH_AES_256_CBC_SHA256       DHE-RSA-AES256-SHA256
 TLS_DHE_RSA_WITH_AES_128_GCM_SHA256       DHE-RSA-AES128-GCM-SHA256
 TLS_DHE_RSA_WITH_AES_256_GCM_SHA384       DHE-RSA-AES256-GCM-SHA384

 TLS_DHE_DSS_WITH_AES_128_CBC_SHA256       DHE-DSS-AES128-SHA256
 TLS_DHE_DSS_WITH_AES_256_CBC_SHA256       DHE-DSS-AES256-SHA256
 TLS_DHE_DSS_WITH_AES_128_GCM_SHA256       DHE-DSS-AES128-GCM-SHA256
 TLS_DHE_DSS_WITH_AES_256_GCM_SHA384       DHE-DSS-AES256-GCM-SHA384

 TLS_ECDH_RSA_WITH_AES_128_CBC_SHA256      ECDH-RSA-AES128-SHA256
 TLS_ECDH_RSA_WITH_AES_256_CBC_SHA384      ECDH-RSA-AES256-SHA384
 TLS_ECDH_RSA_WITH_AES_128_GCM_SHA256      ECDH-RSA-AES128-GCM-SHA256
 TLS_ECDH_RSA_WITH_AES_256_GCM_SHA384      ECDH-RSA-AES256-GCM-SHA384

 TLS_ECDH_ECDSA_WITH_AES_128_CBC_SHA256    ECDH-ECDSA-AES128-SHA256
 TLS_ECDH_ECDSA_WITH_AES_256_CBC_SHA384    ECDH-ECDSA-AES256-SHA384
 TLS_ECDH_ECDSA_WITH_AES_128_GCM_SHA256    ECDH-ECDSA-AES128-GCM-SHA256
 TLS_ECDH_ECDSA_WITH_AES_256_GCM_SHA384    ECDH-ECDSA-AES256-GCM-SHA384

 TLS_ECDHE_RSA_WITH_AES_128_CBC_SHA256     ECDHE-RSA-AES128-SHA256
 TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA384     ECDHE-RSA-AES256-SHA384
 TLS_ECDHE_RSA_WITH_AES_128_GCM_SHA256     ECDHE-RSA-AES128-GCM-SHA256
 TLS_ECDHE_RSA_WITH_AES_256_GCM_SHA384     ECDHE-RSA-AES256-GCM-SHA384

 TLS_ECDHE_ECDSA_WITH_AES_128_CBC_SHA256   ECDHE-ECDSA-AES128-SHA256
 TLS_ECDHE_ECDSA_WITH_AES_256_CBC_SHA384   ECDHE-ECDSA-AES256-SHA384
 TLS_ECDHE_ECDSA_WITH_AES_128_GCM_SHA256   ECDHE-ECDSA-AES128-GCM-SHA256
 TLS_ECDHE_ECDSA_WITH_AES_256_GCM_SHA384   ECDHE-ECDSA-AES256-GCM-SHA384

 TLS_DH_anon_WITH_AES_128_CBC_SHA256       ADH-AES128-SHA256
 TLS_DH_anon_WITH_AES_256_CBC_SHA256       ADH-AES256-SHA256
 TLS_DH_anon_WITH_AES_128_GCM_SHA256       ADH-AES128-GCM-SHA256
 TLS_DH_anon_WITH_AES_256_GCM_SHA384       ADH-AES256-GCM-SHA384
 TLS_ECDHE_ECDSA_WITH_CAMELLIA_128_CBC_SHA256 ECDHE-ECDSA-CAMELLIA128-SHA256
 TLS_ECDHE_ECDSA_WITH_CAMELLIA_256_CBC_SHA384 ECDHE-ECDSA-CAMELLIA256-SHA384
 TLS_ECDH_ECDSA_WITH_CAMELLIA_128_CBC_SHA256  ECDH-ECDSA-CAMELLIA128-SHA256
 TLS_ECDH_ECDSA_WITH_CAMELLIA_256_CBC_SHA384  ECDH-ECDSA-CAMELLIA256-SHA384
 TLS_ECDHE_RSA_WITH_CAMELLIA_128_CBC_SHA256   ECDHE-RSA-CAMELLIA128-SHA256
 TLS_ECDHE_RSA_WITH_CAMELLIA_256_CBC_SHA384   ECDHE-RSA-CAMELLIA256-SHA384
 TLS_ECDH_RSA_WITH_CAMELLIA_128_CBC_SHA256    ECDH-RSA-CAMELLIA128-SHA256
 TLS_ECDH_RSA_WITH_CAMELLIA_256_CBC_SHA384    ECDH-RSA-CAMELLIA256-SHA384

Now let’s see what may potentially be good from TLSv1.1 perspective (from NIST SP8000-52 rev1):

TLS_RSA_WITH_3DES_EDE_CBC_SHA           DES-CBC3-SHA
TLS_RSA_WITH_AES_128_CBC_SHA            AES128-SHA

Here’s a problem though per OpenSSL man page:

Untitled

If you’re using OpenSSL, how do you ensure that the browser is not negotiating the vulnerable TLSv1.0 ciphers? The only real answer seems to be by providing a cipher order for negotiation and hoping the client doesn’t cheat.  Most likely, the browser will negotiate a better cipher when it exists in the server and on the client and you’d avert the possibility of negotiation of a bad cipher.

According to experts, anything that uses CBC is inherently broken.  But disabling TLSv1.0 may make the server inaccessible to various older Android devices.  Also, if you’re using older Java Development Kits (JDK7 and below), do remember that the default ciphers may not hit the spot for PCI.

There’s an excellent site to help you configure each type of the server so you could become PCI compliant. This is an excellent site by Ivan Ristic to test your Internet-facing servers for configuration of SSL/TLS encryption.

In conclusion, configure browsers to minimally allow TLSv1.1 and configure servers to use TLSv1.2 to be PCI DSS compliant.  The road to TLSv1.1 compatibility and PCI DSS is filled with potholes and death-falls so do it at your own risk.